Security you can verify.
What data we store, how we protect it and how you can check the key points yourself with independent services.
How we protect your account and your data
Encrypted storage
Your playlists and credentials are stored encrypted in the database, with the key kept separately. To be clear: our server has to decrypt your sources to play them for you; this is not end-to-end encryption.
AES-256-GCM, favorites included
Passwords never in plain text
Even someone who got hold of the database couldn't read any passwords from it.
Passwords as scrypt hash, 2FA secrets encrypted, sessions only as a hash
Passkeys and two-factor
Sign in with a passkey, which protects you from fake sign-in pages, or with a password and an authenticator app.
Admin area only with a fresh 2FA confirmation
Protection against attacks
The connection is always encrypted, other sites can't trigger anything in your name, and anyone trying passwords is slowed down.
HTTPS with HSTS, Content Security Policy, CSRF checks, rate limits, SSRF protection in the stream proxy
Operations and backups
Servers in Germany (EU), an encrypted backup every day, and the restore is tested every week.
Streamline reachable from outside only via HTTPS, automatic security updates, every update first goes through tests, vulnerability and secret scans
You're in control
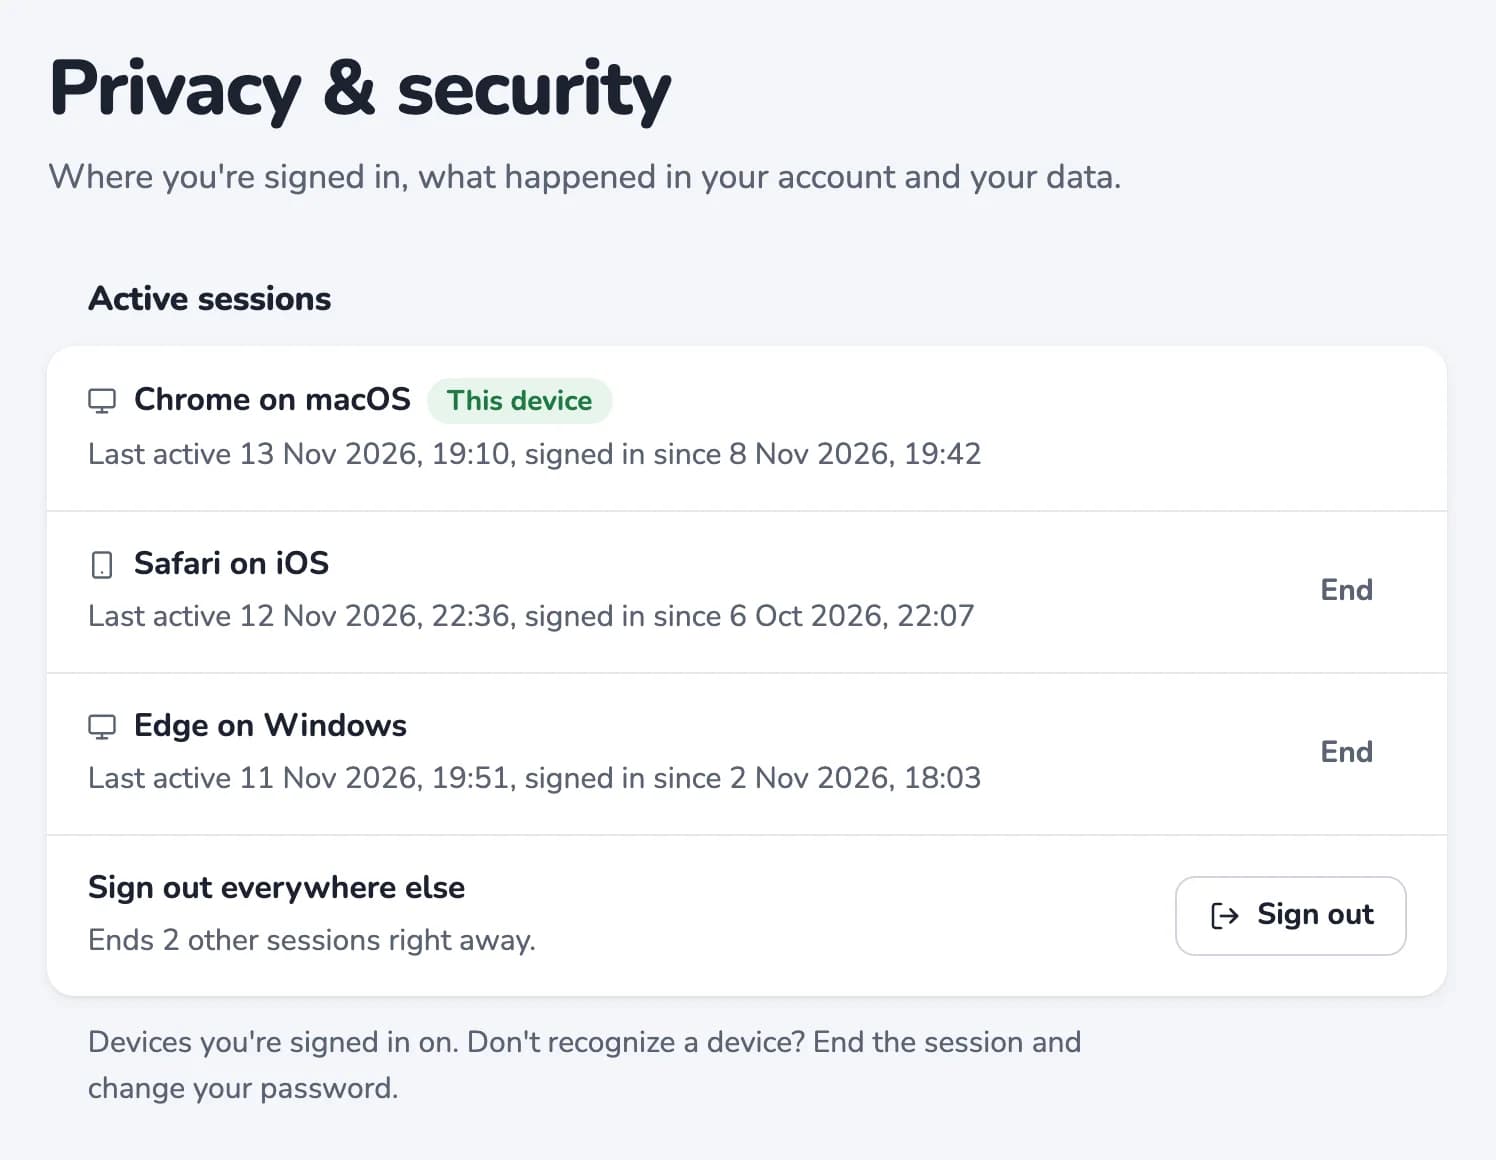
You see your active sessions and end them, read the log of your sign-ins, and download your data or delete your account, right in Settings.
Deleting requires your password


What data we store
Complete and without fine print. Legal details are in the privacy policy.
| Data | Purpose | Protection | Retention |
|---|---|---|---|
| Email, name | Account, sign-in, invoices | Access only for you and support | Until account deletion |
| Password, 2FA, passkeys | Sign-in | scrypt hash, encrypted, public keys only | Until account deletion |
| Playlists and credentials | Playback on all your devices | Encrypted with AES-256-GCM | Until you delete them |
| Sessions | Staying signed in | Stored only as a hash, visible to you and can be ended | Until you sign out, at most 60 days |
| Security log | Protection against abuse | Visible only to you | 90 days |
| Subscription and invoices | Billing | Payment details only at Stripe, never with us | 10 years (tax law) |
| Support tickets | Help with problems | Only for you and support | Until account deletion |
| Server logs | Troubleshooting, attack prevention | No outside access, without address parameters containing credentials | Short, rotated and deleted automatically |
| Anonymous usage statistics | Improving the website and the app | No cookies, no IP address, no link to your account | 13 months |
| Enhanced statistics (only with consent) | Improving the website and the app | Only after you agree in the cookie banner, IP address shortened after 30 days, can be withdrawn at any time | 13 months |
Service providers that process data on our behalf: Hetzner Online GmbH (hosting) and Stripe (payment). Tracking only with your consent, no ad networks, no selling of data. We measure reach on our own server: anonymously and without cookies unless you consent, enhanced only if you agree.
Check it yourself
- Qualys SSL LabsChecks the encryption and certificate of the connection. Target: A+. (opens in a new tab)
- securityheaders.comChecks the protective headers against clickjacking, XSS and data leaks. (opens in a new tab)
- Mozilla HTTP ObservatoryIndependent web security rating by Mozilla. (opens in a new tab)
- internet.nlChecks modern internet standards such as IPv6, DNSSEC, HTTPS and secure headers. (opens in a new tab)
Automated checks
Our server checks itself regularly: headers, TLS and dependencies weekly, the backup daily, and a test restore weekly.
| Check | Result | Last checked |
|---|---|---|
| Security headers | Passed | 16 Nov 2026, 05:00 |
| TLS certificate | Passed | 16 Nov 2026, 05:00 |
| Only modern TLS versions | Passed | 16 Nov 2026, 05:00 |
| Dependencies without known vulnerabilities | Passed | 16 Nov 2026, 05:00 |
| Encrypted backup | Passed | 16 Nov 2026, 02:31 |
| Restore tested | Passed | 15 Nov 2026, 04:00 |
| Service reachable | Passed | 16 Nov 2026, 05:00 |
Found a security vulnerability?
Thanks for your help. Please report vulnerabilities confidentially to contact@navoryx.site (details also in our security.txt). We confirm receipt within three business days, keep you updated on the fix and credit you by name if you like. Please do not access other people's data or disrupt the service while doing so.